
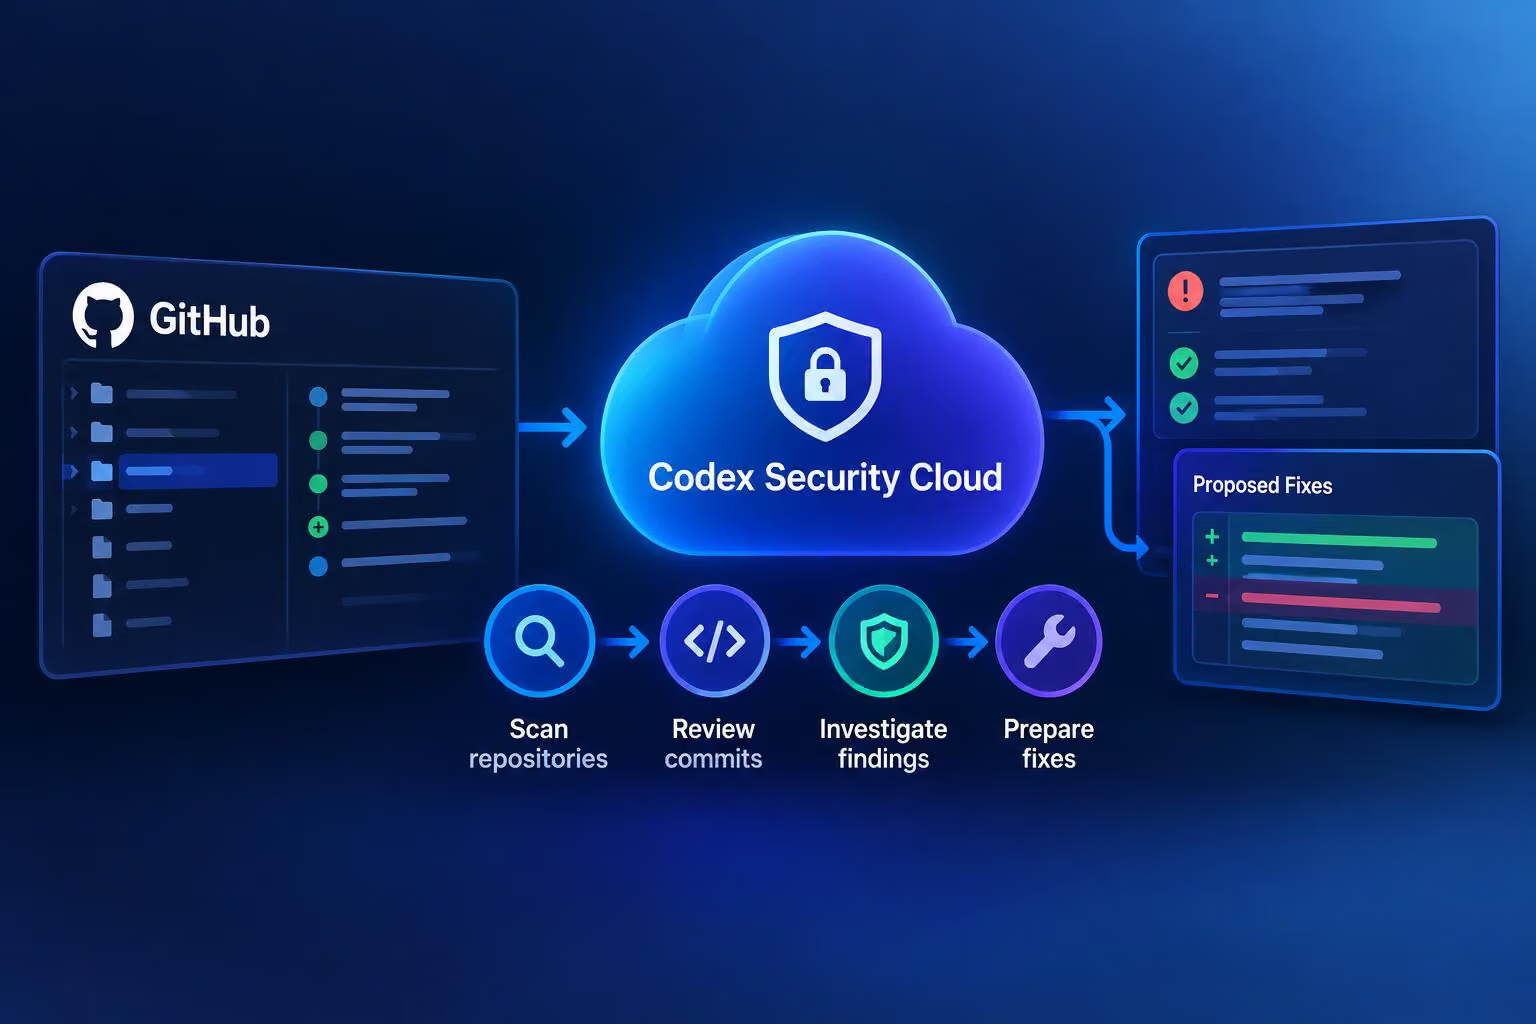
OpenAI says Codex Security Cloud is getting a major upgrade that adds default access to cyber-capable models through Daybreak Blue. The company describes a workflow that scans entire GitHub repositories, continues reviewing new commits, investigates and deduplicates findings, and prepares fixes for human review—even when the user's laptop is closed.
What OpenAI announced
The announcement does not explain what the cyber-capable models are beyond that description or how they are used inside Codex Security Cloud.
The post presents the service as a continuing repository-security workflow rather than a one-time scan. It says Codex Security Cloud can examine an entire GitHub repository and keep reviewing new commits after the initial scan. That could help keep security checks connected to ongoing code changes, but the announcement does not provide details about supported languages, repository limits, coverage or detection performance.
How the reported workflow handles findings
In a post on X, @OpenAI says Codex Security Cloud investigates findings and deduplicates them. In practical terms, that describes two separate stages: investigating findings to provide more context, and reducing duplicate reports so related issues are not presented repeatedly. The post does not explain how either process works or how the service determines that findings are duplicates.
The announcement also says the service prepares fixes for review. That wording describes proposed remediation for a person to assess; it does not say that fixes are automatically applied. The source likewise does not specify the review controls, generated patch format or approval process.
Where the plugin is available
OpenAI says Codex Security Cloud is available as a plugin in Codex desktop and on the web. The announcement does not clarify whether access is universal, whether additional eligibility requirements apply, or whether the plugin has different capabilities across those surfaces.
The post provides no pricing, rollout schedule, benchmarks, independent testing or technical implementation details. Its supported description is limited to the reported workflow: scanning repositories, reviewing new commits, investigating and deduplicating findings, and preparing fixes for review while work can continue when a user's laptop is closed.
0 comments
No approved comments yet. You can start the conversation.
Leave a comment